Opsin raises $21M to secure the agentic enterprise.
Hear from our founders →

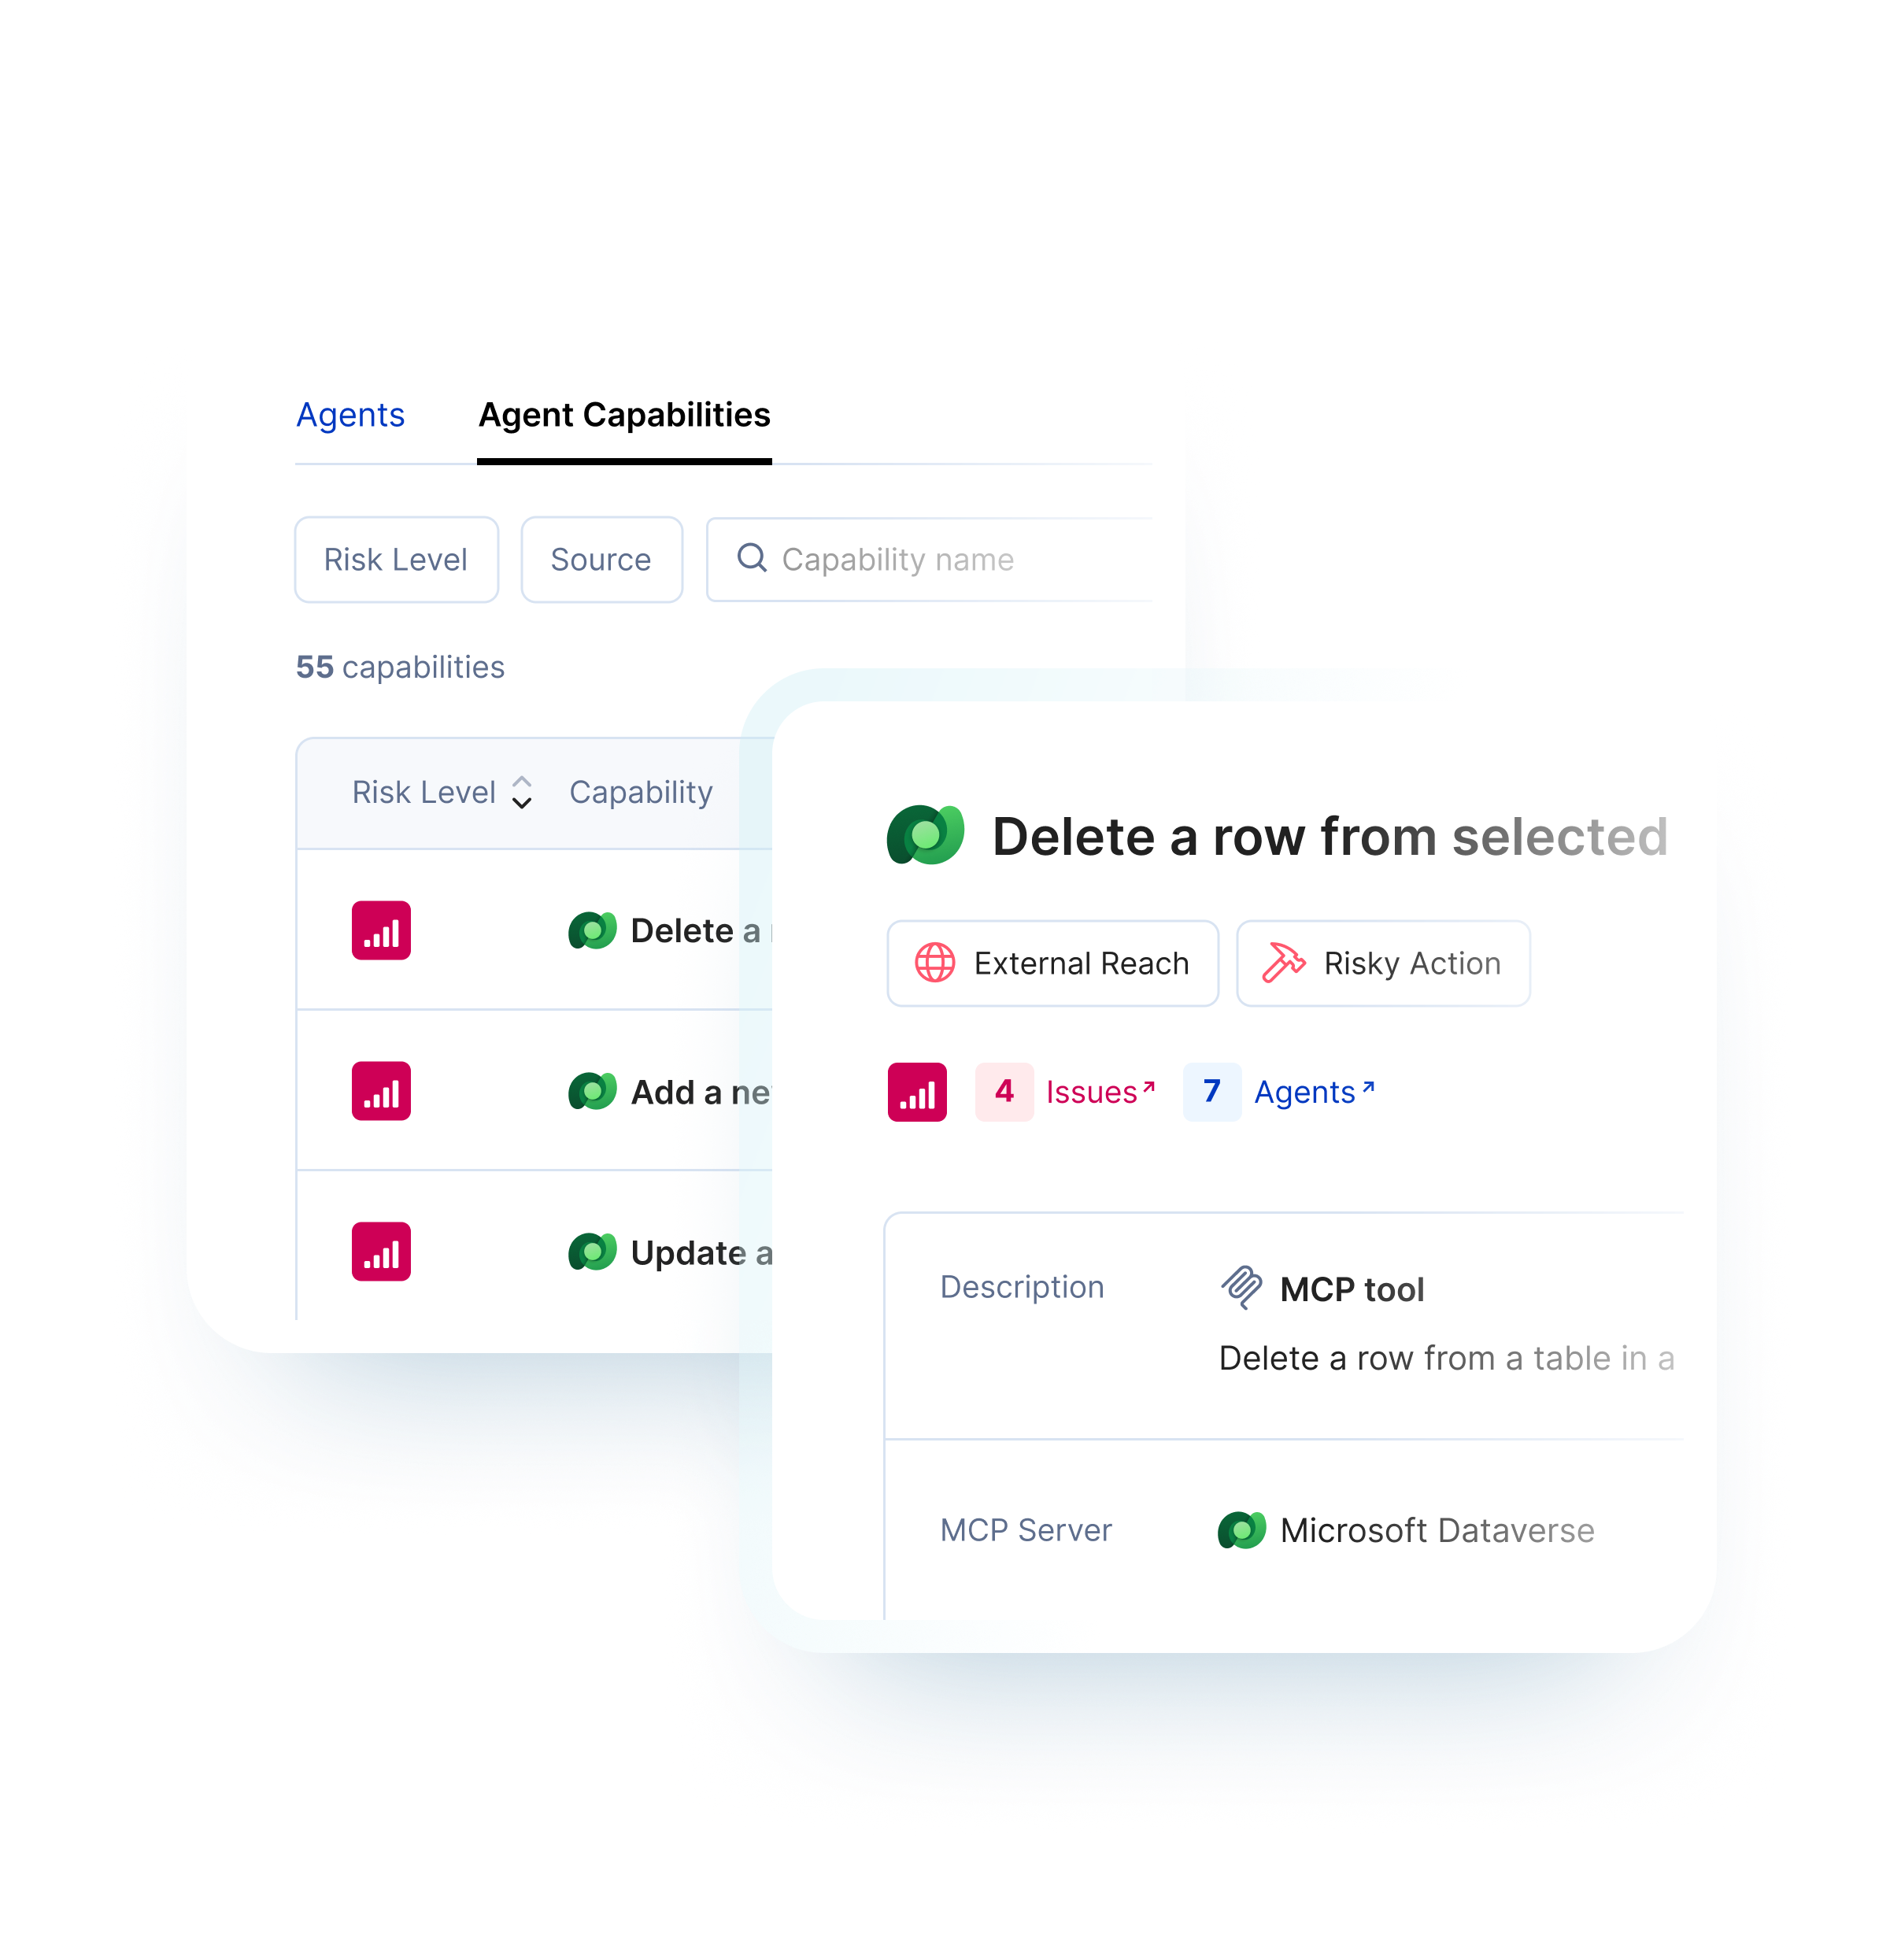







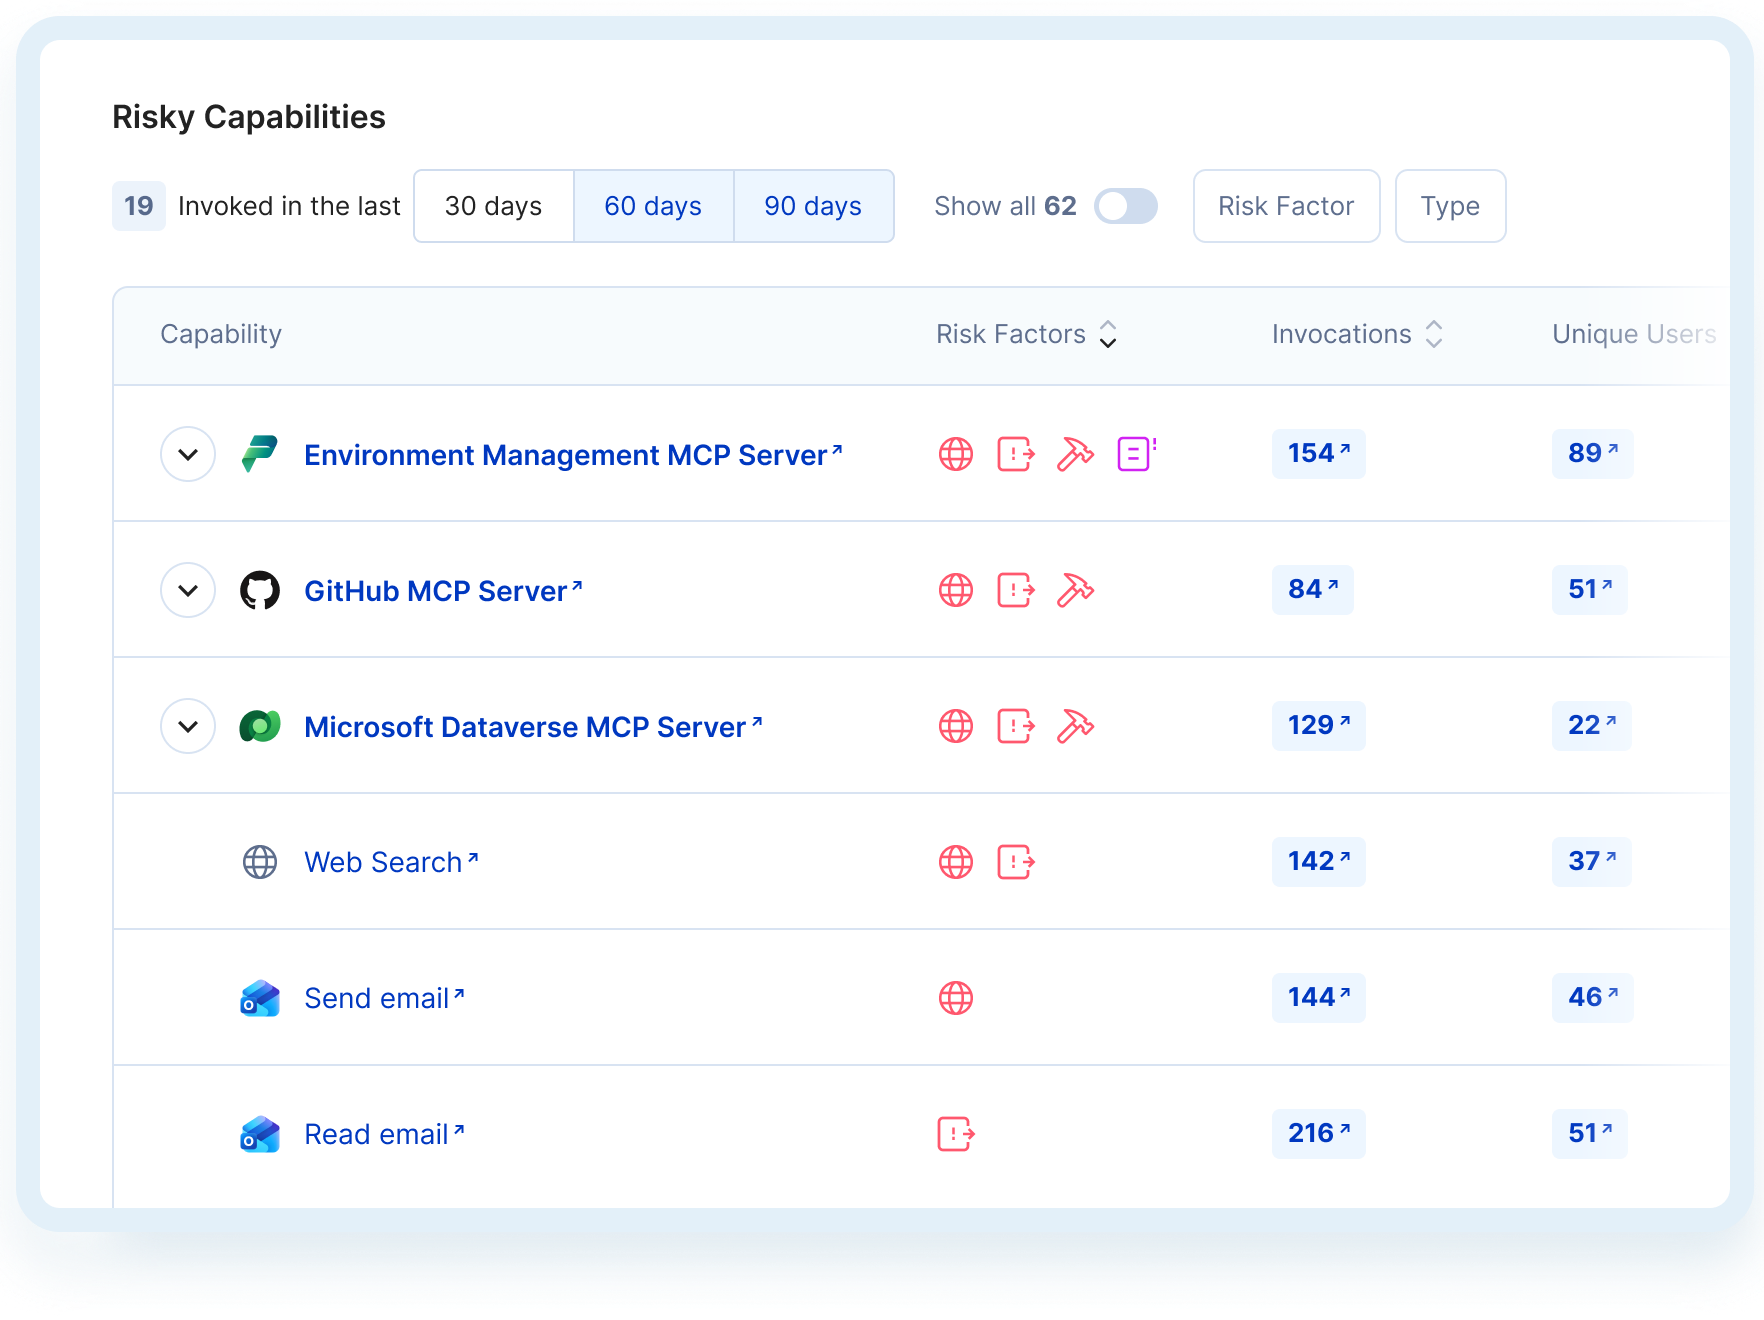
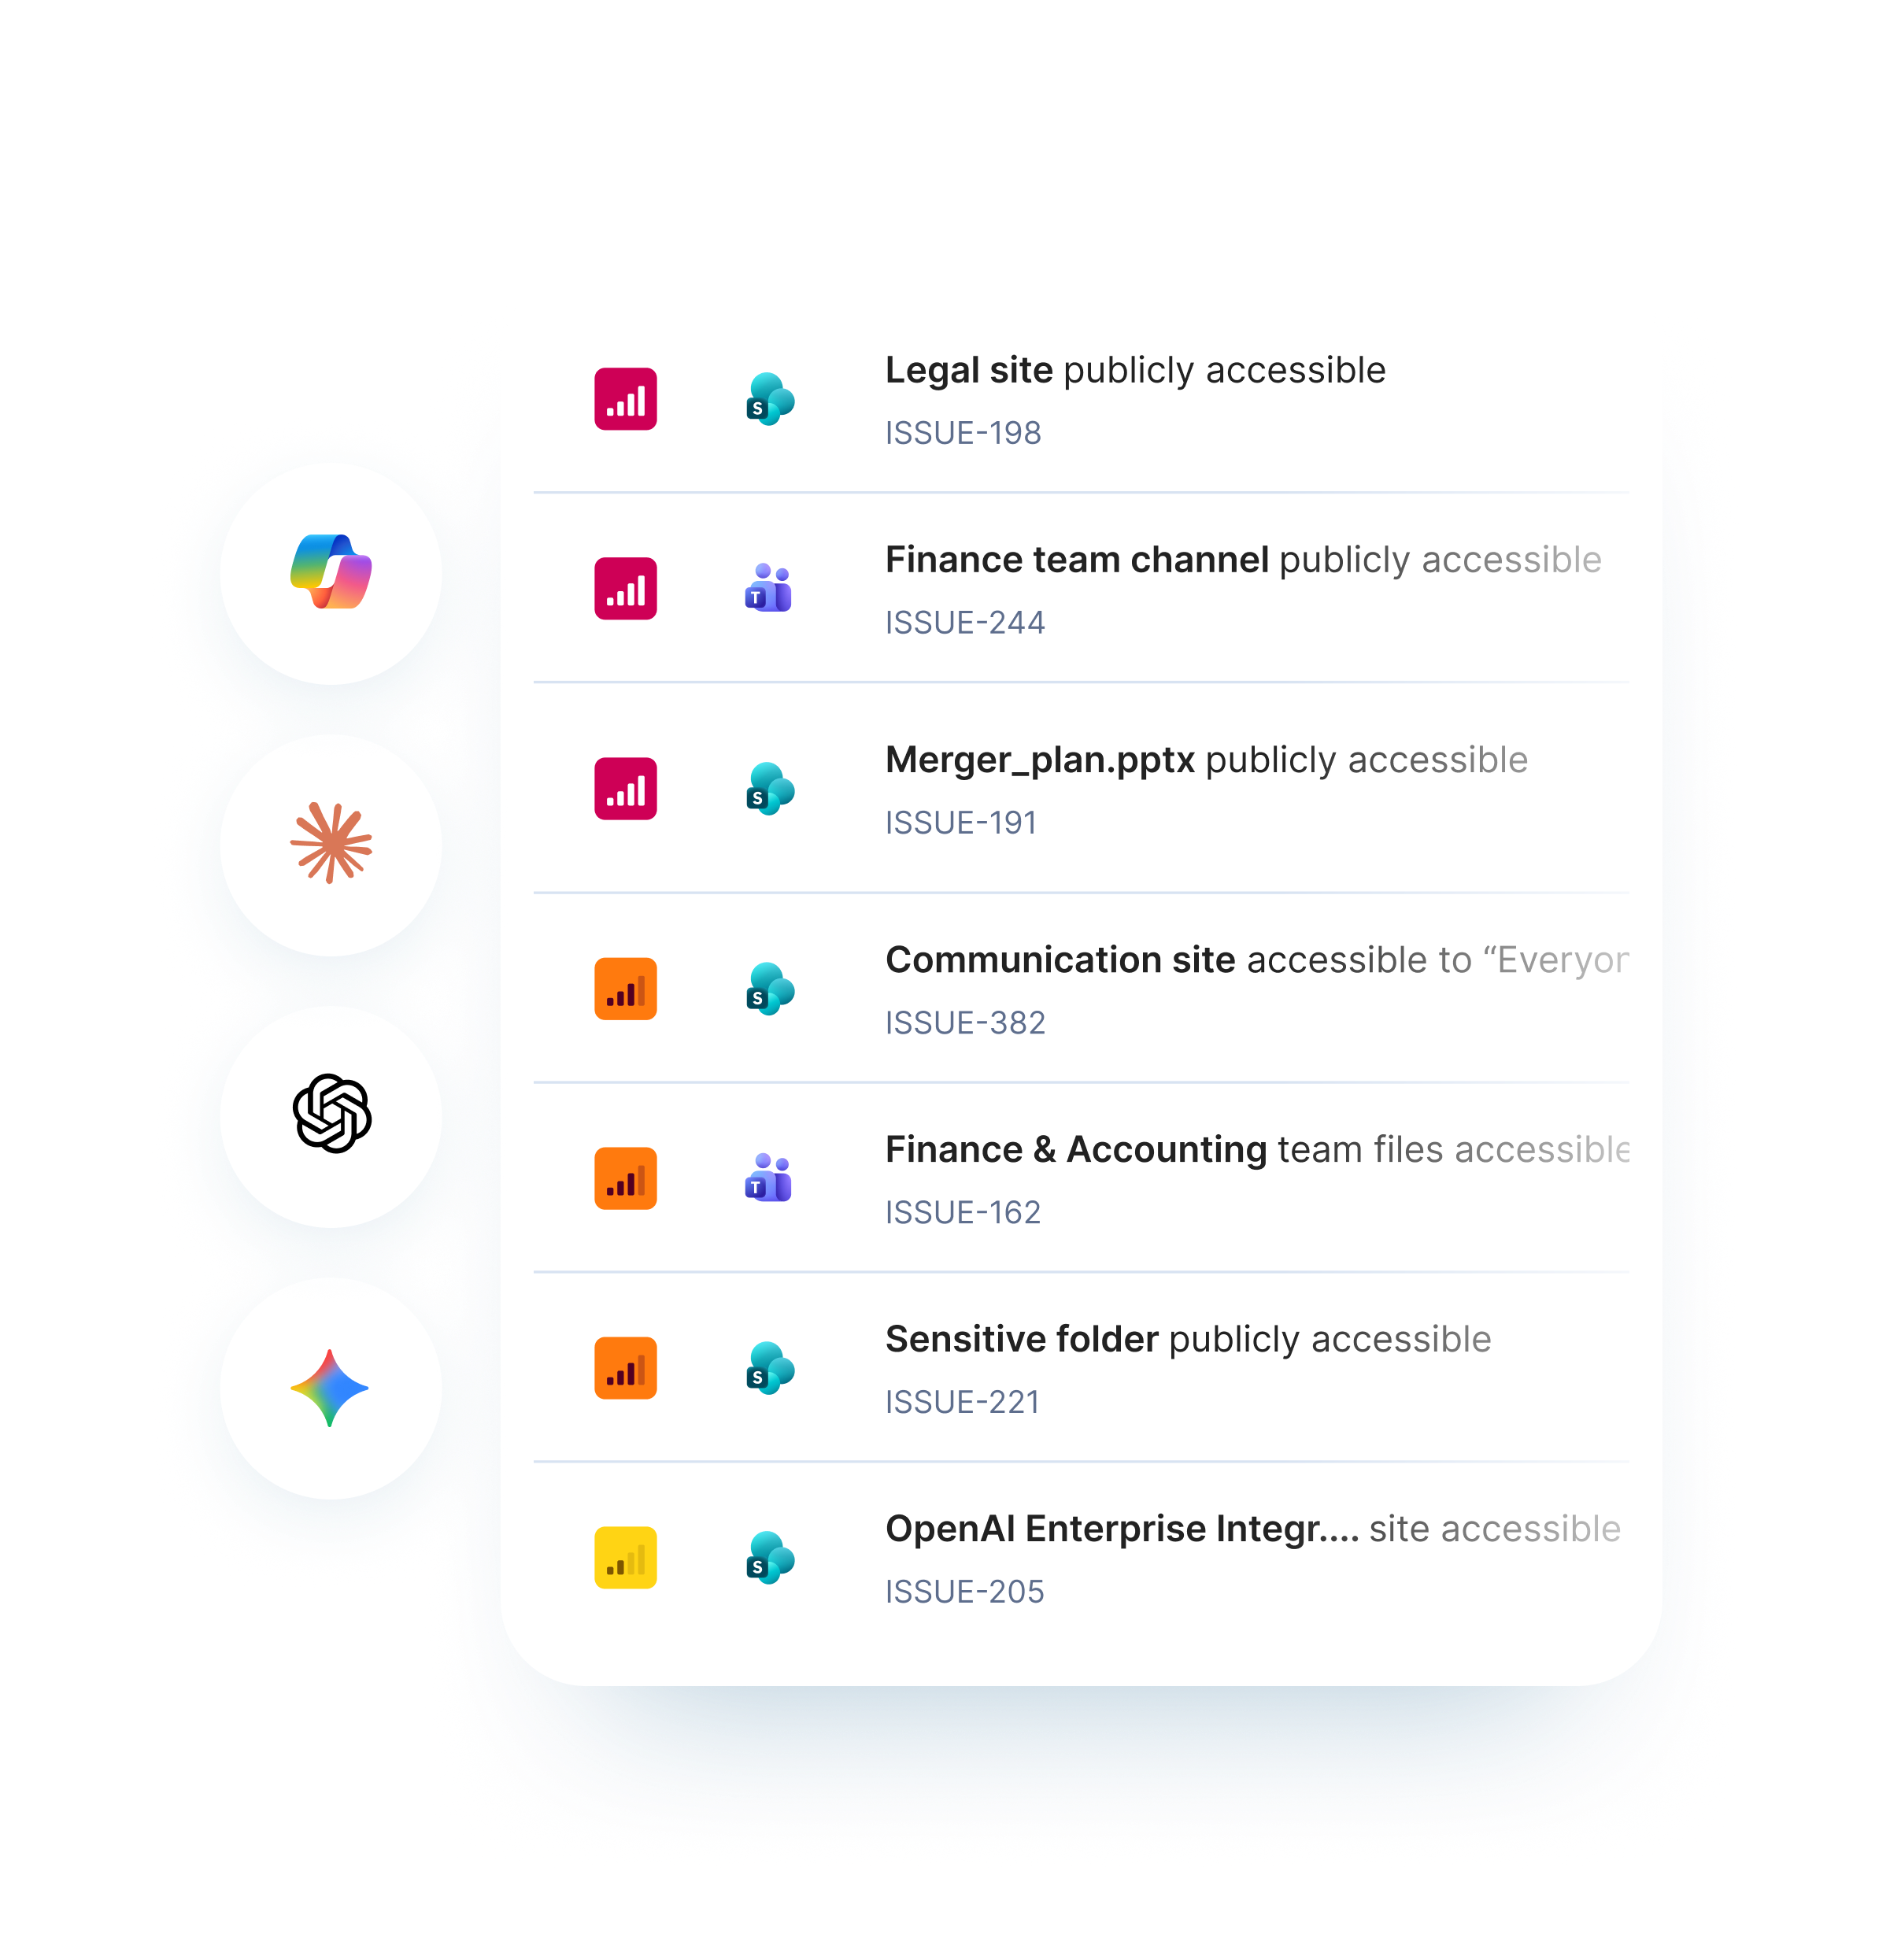
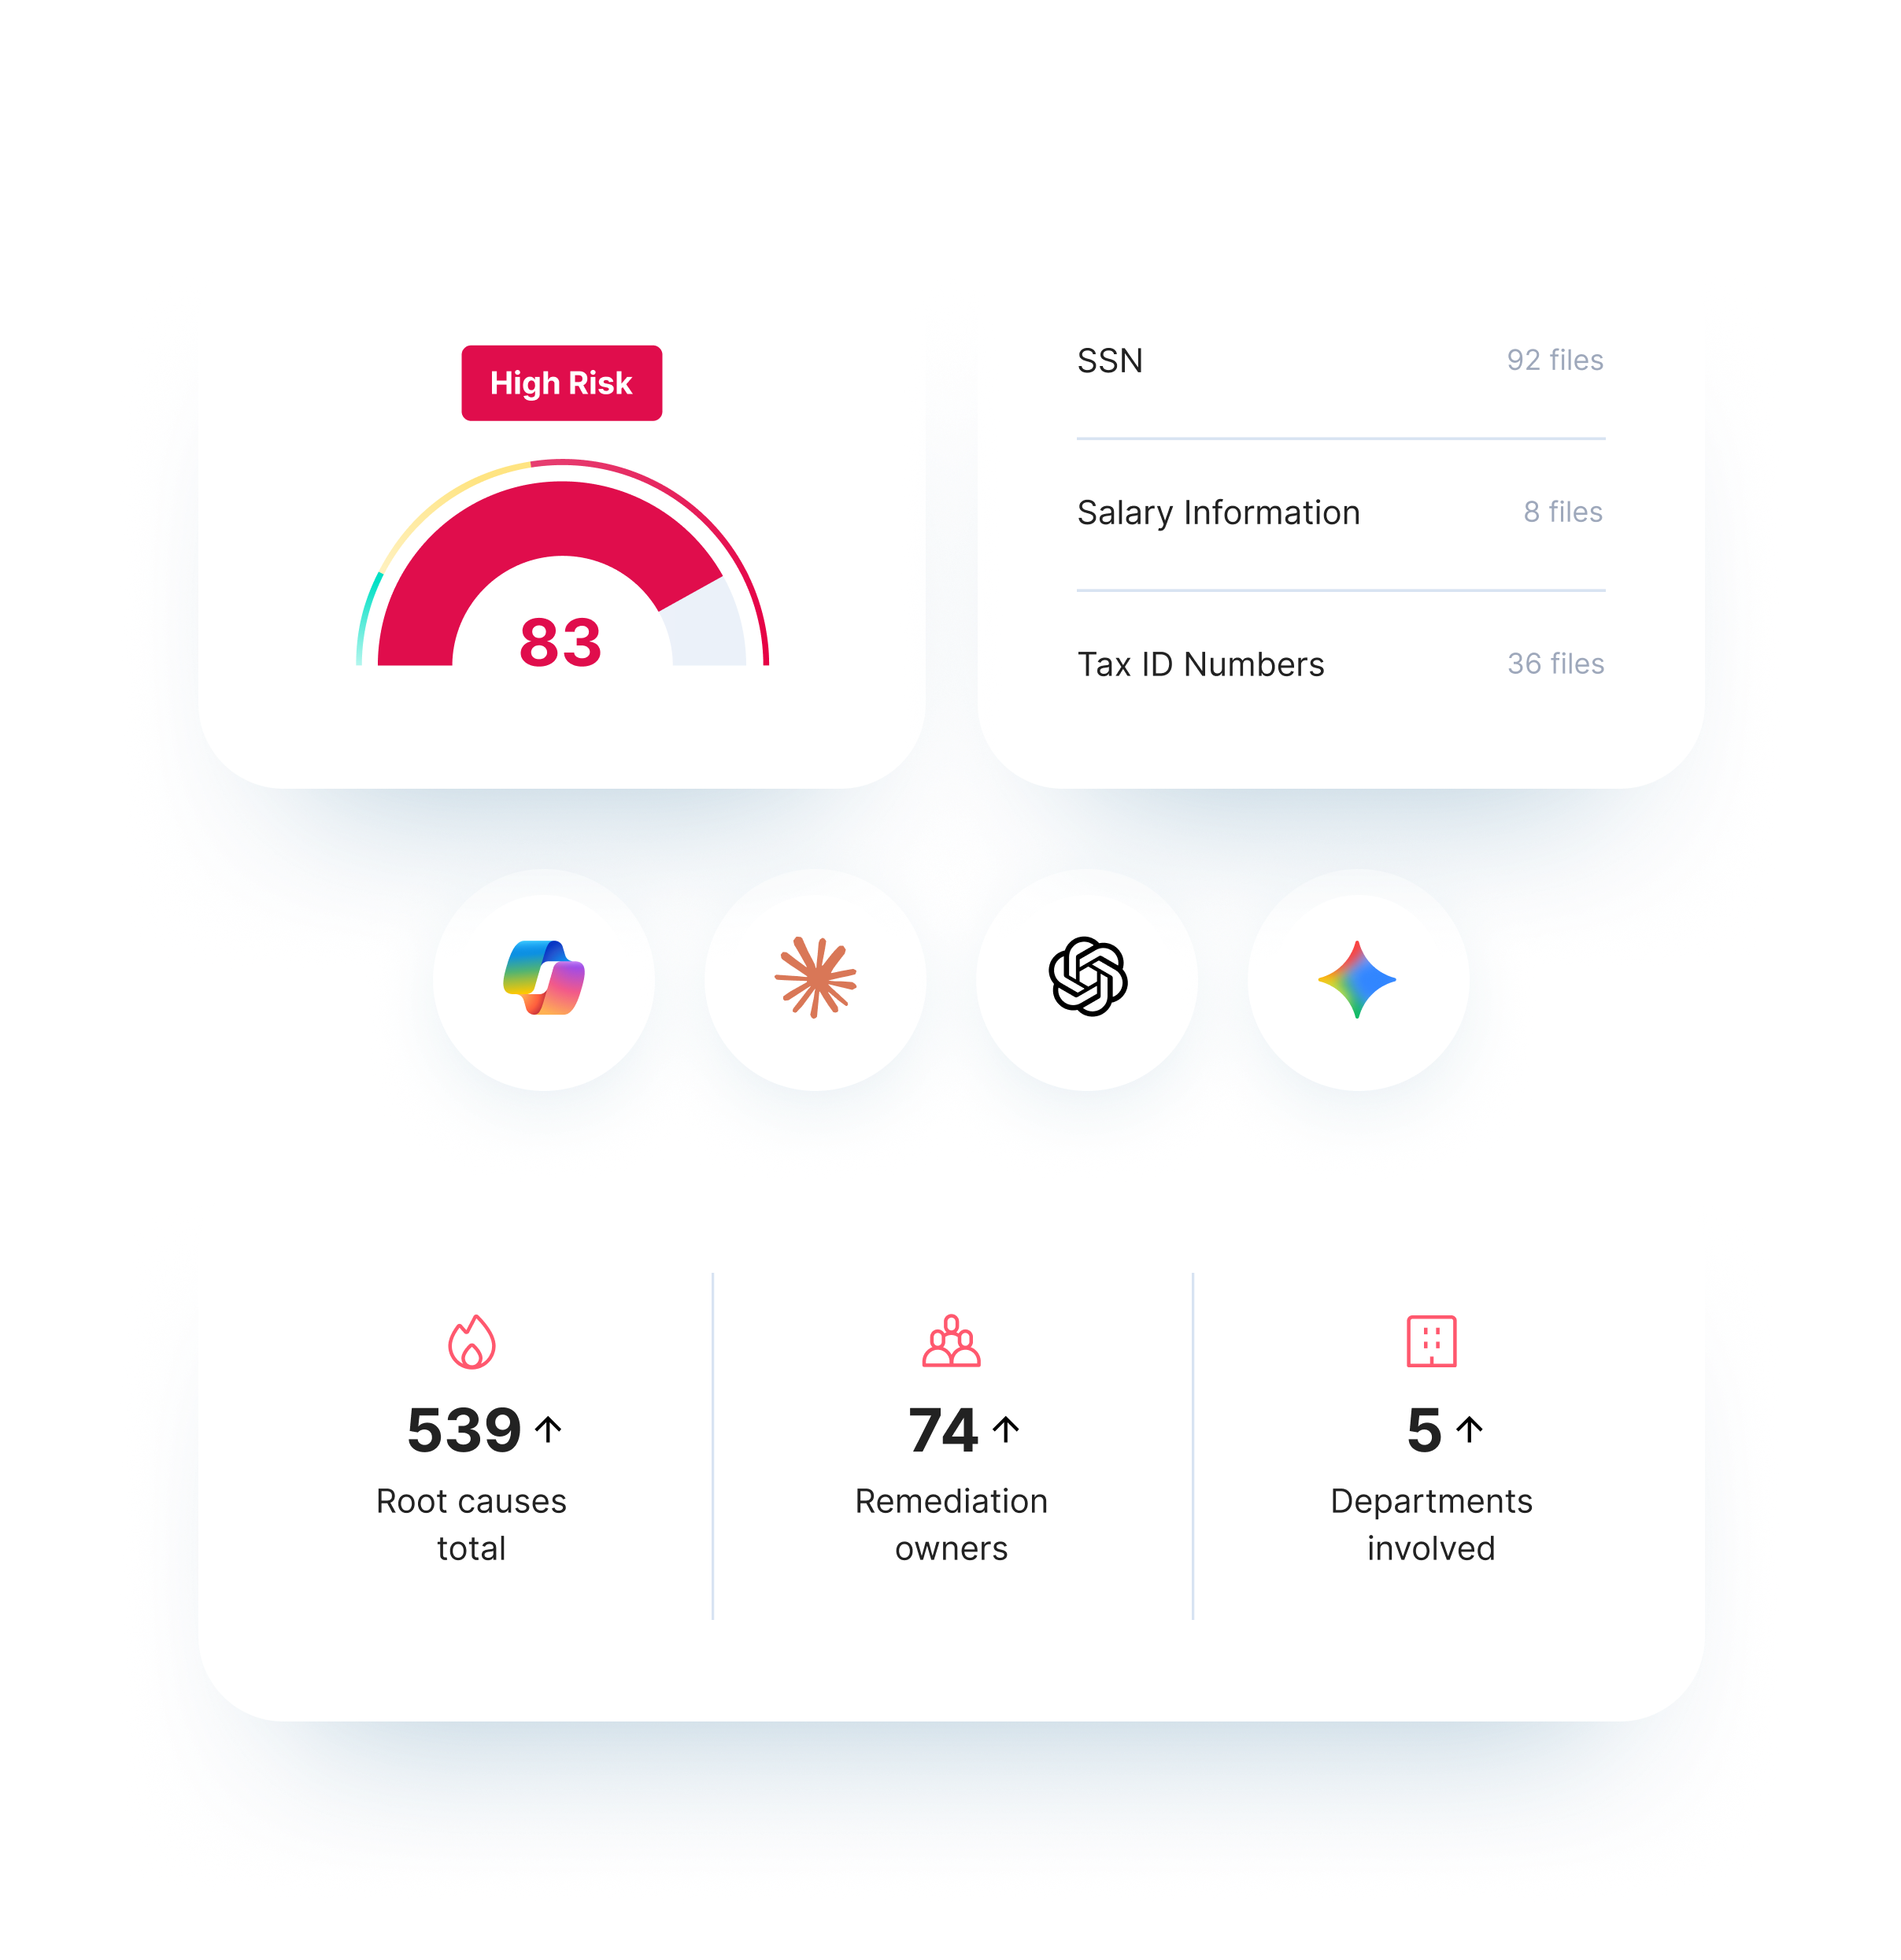
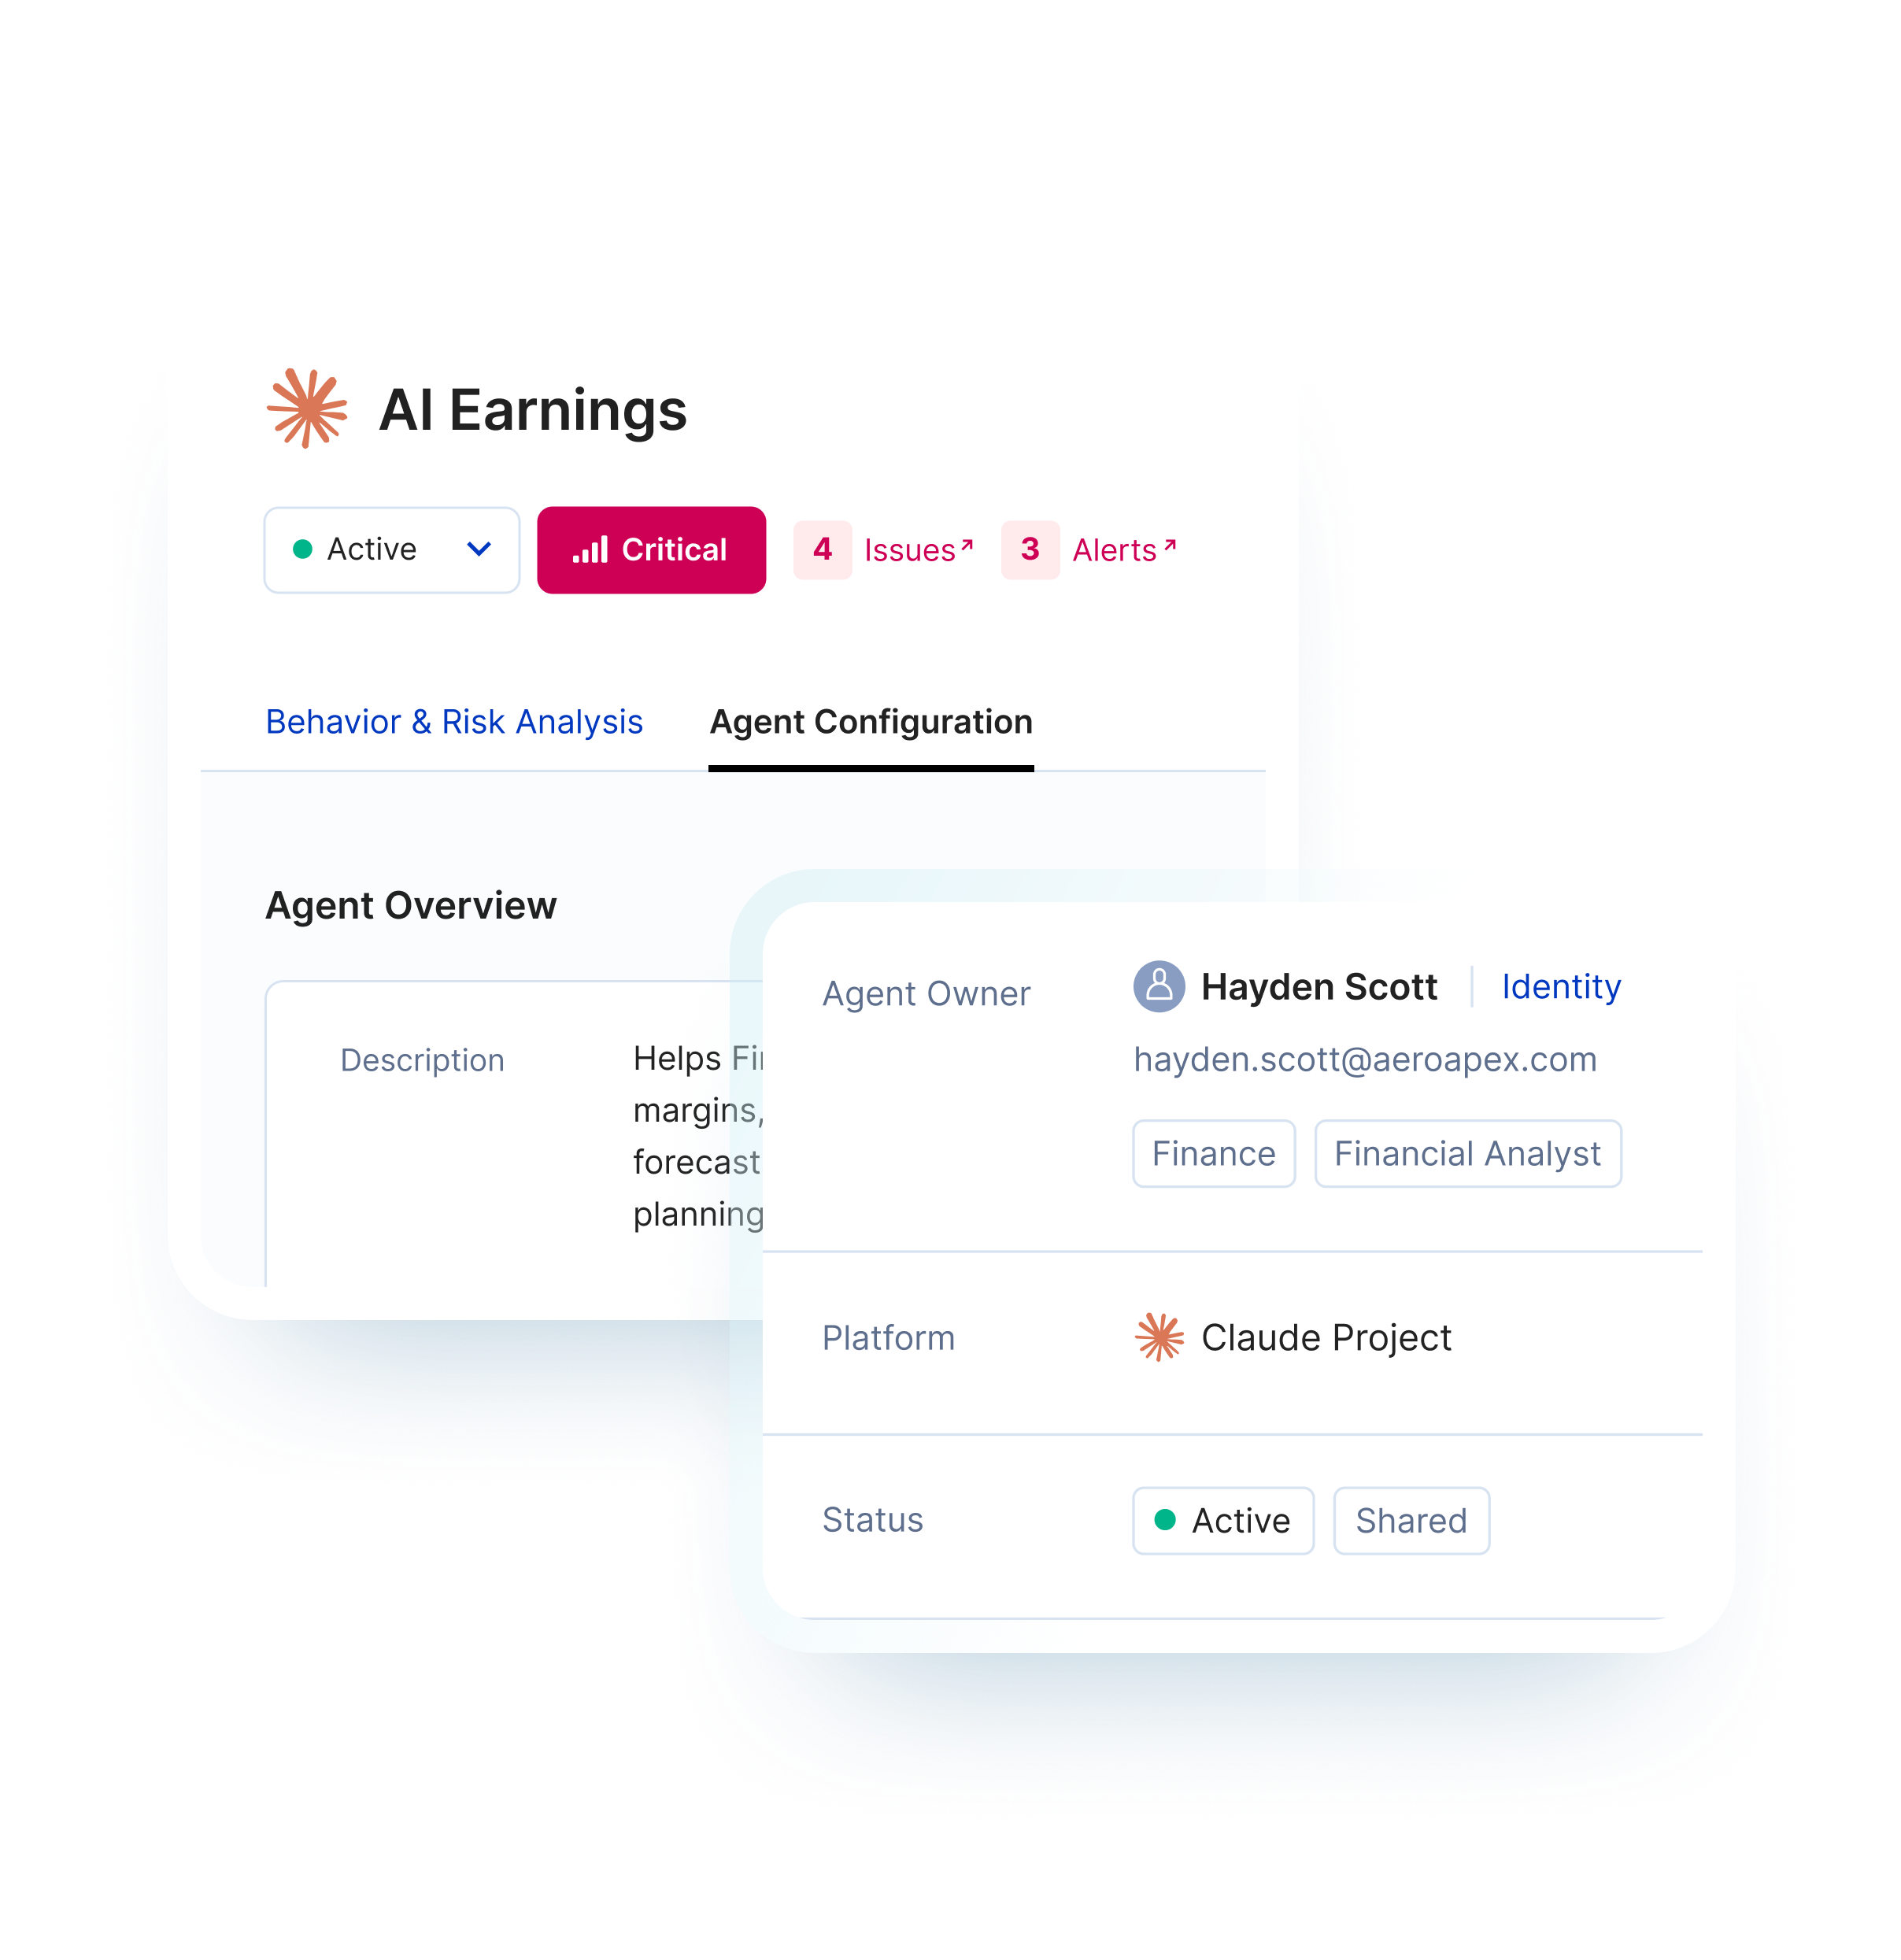

MCP is an open standard that lets AI agents call external tools and data sources such as file systems, databases, and SaaS apps. Every MCP server an agent can invoke extends what that agent can reach, which is why MCP belongs in your security picture.
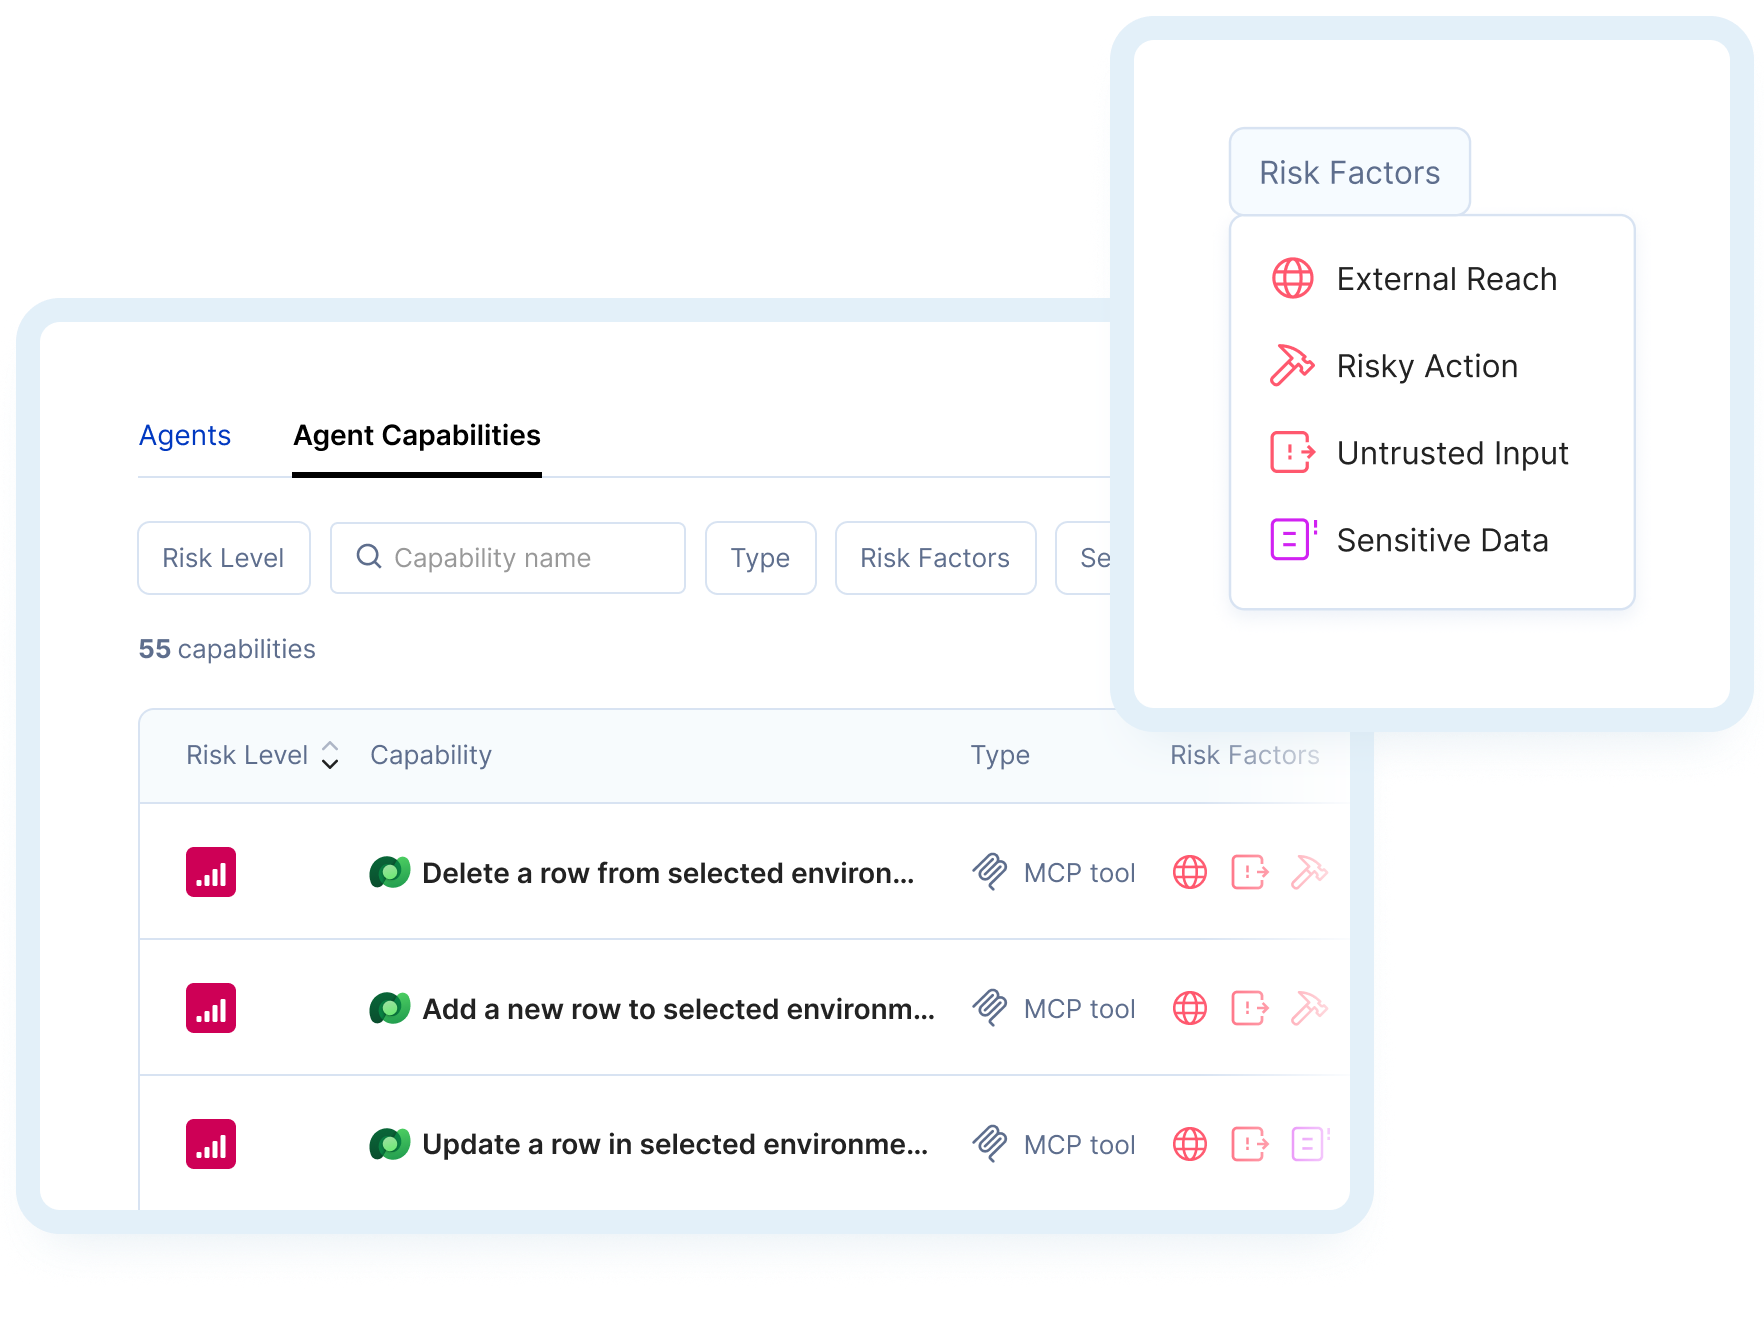
The risks Opsin flags, in order of impact:
For a field guide to how these play out, read The Mushroom Market.
Opsin builds the inventory from enterprise AI platform APIs, with no agents to deploy and no traffic to route. Each tool is classified by capability and mapped to the agents using it, extending the same approach as Agent Discovery.
Yes. Teams can restrict risky MCPs, tag connections that hold sensitive data, and mark reviewed servers as verified. Enforcement then matches how sensitive each connection is, and runtime monitoring catches agents that misuse approved tools.
Very. Opsin found 60% of agents provisioned beyond default settings were granted allow-all access beyond what their tasks required (2026 State of Agentic Adoption Report).
Start with visibility. A free AI Readiness Assessment shows every MCP server your agents can invoke, delivered within 24 hours.
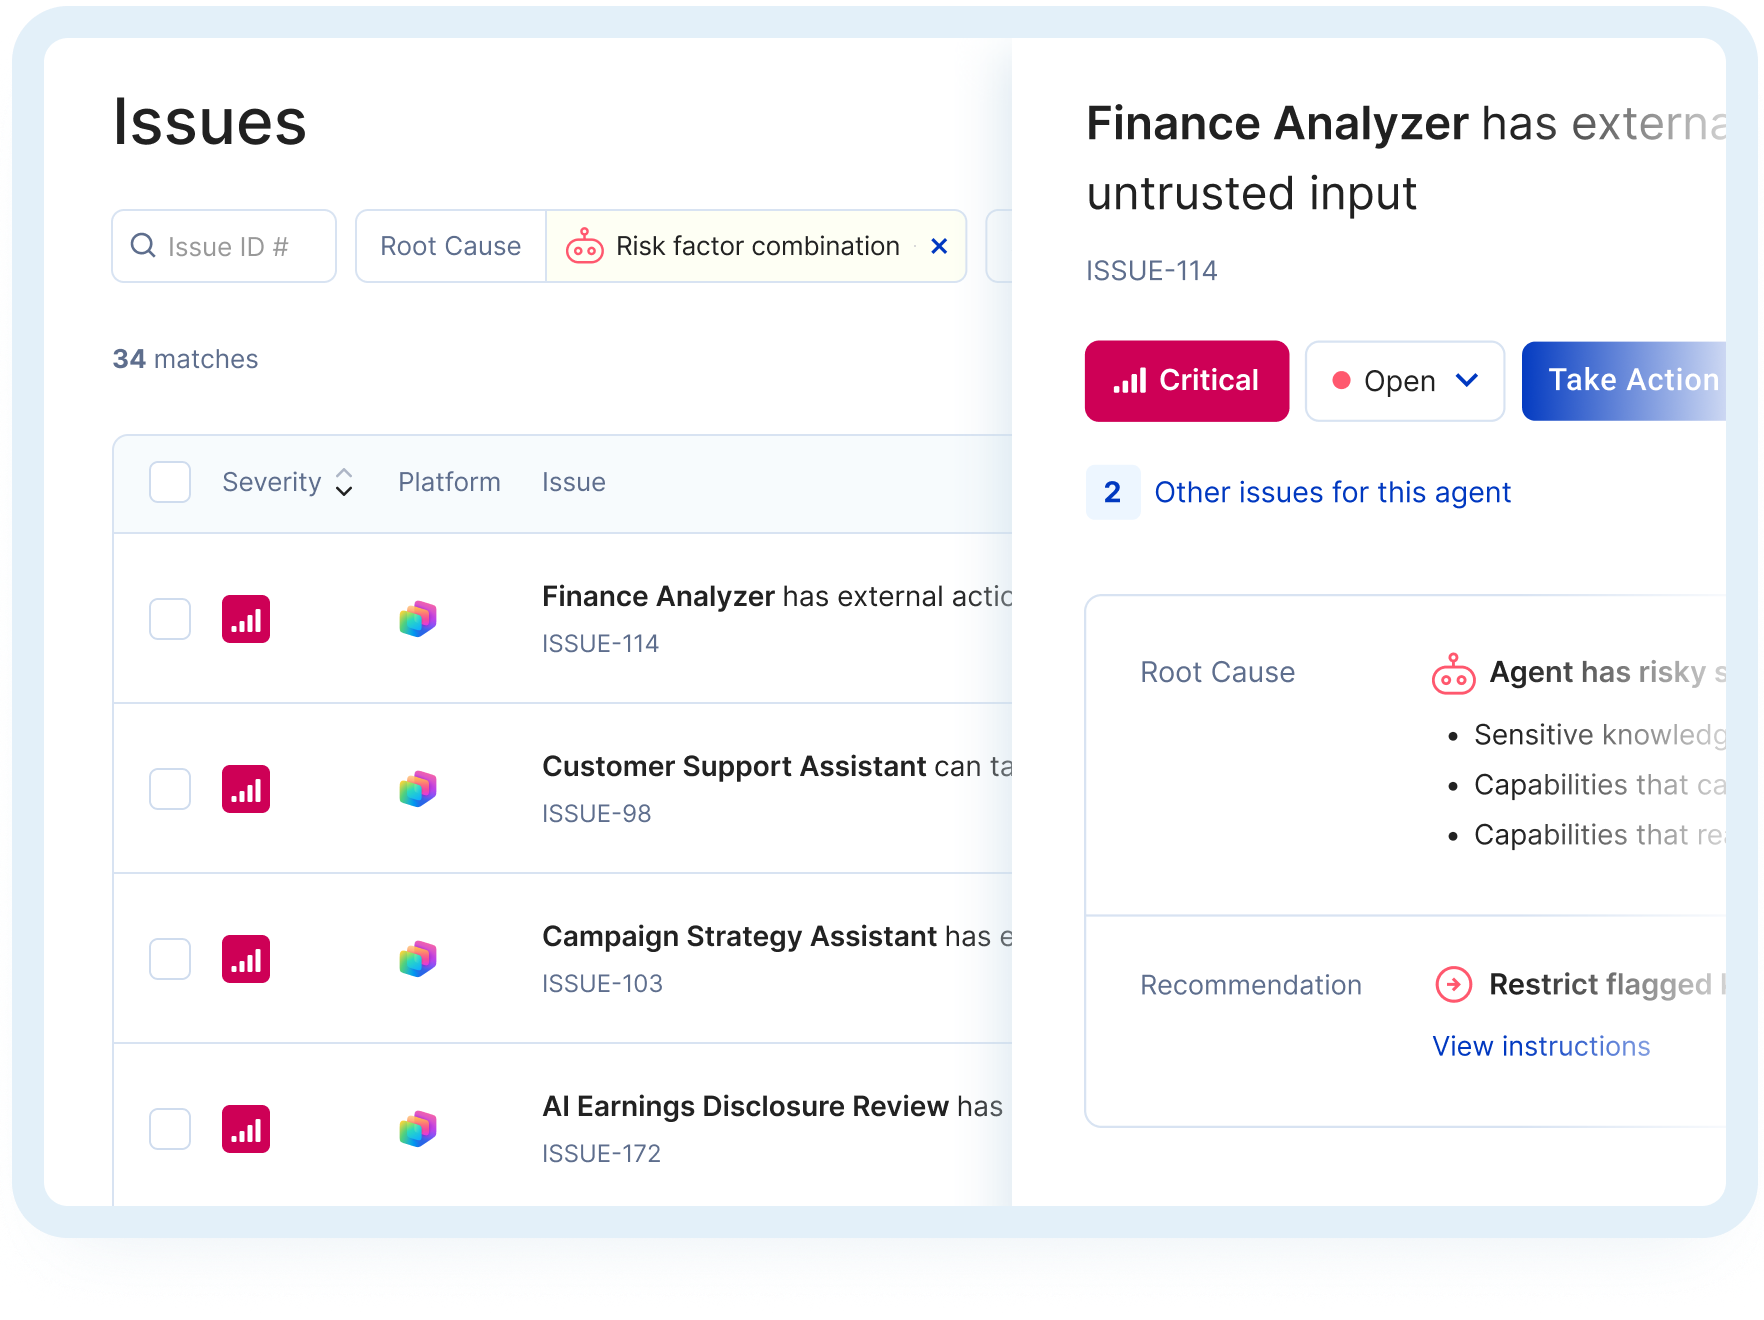
Opsin shows MCP servers in context: which agents use them, what they can reach and what they can change. The inventory comes from platform APIs with nothing to deploy. Each tool is classified by capability and exposure, your team tags the sensitive connections, and you restrict, tag or verify MCPs from one view. MCP risk shows up at runtime too; see Agent Runtime Security.