Opsin raises $21M to secure the agentic enterprise.
Hear from our founders →

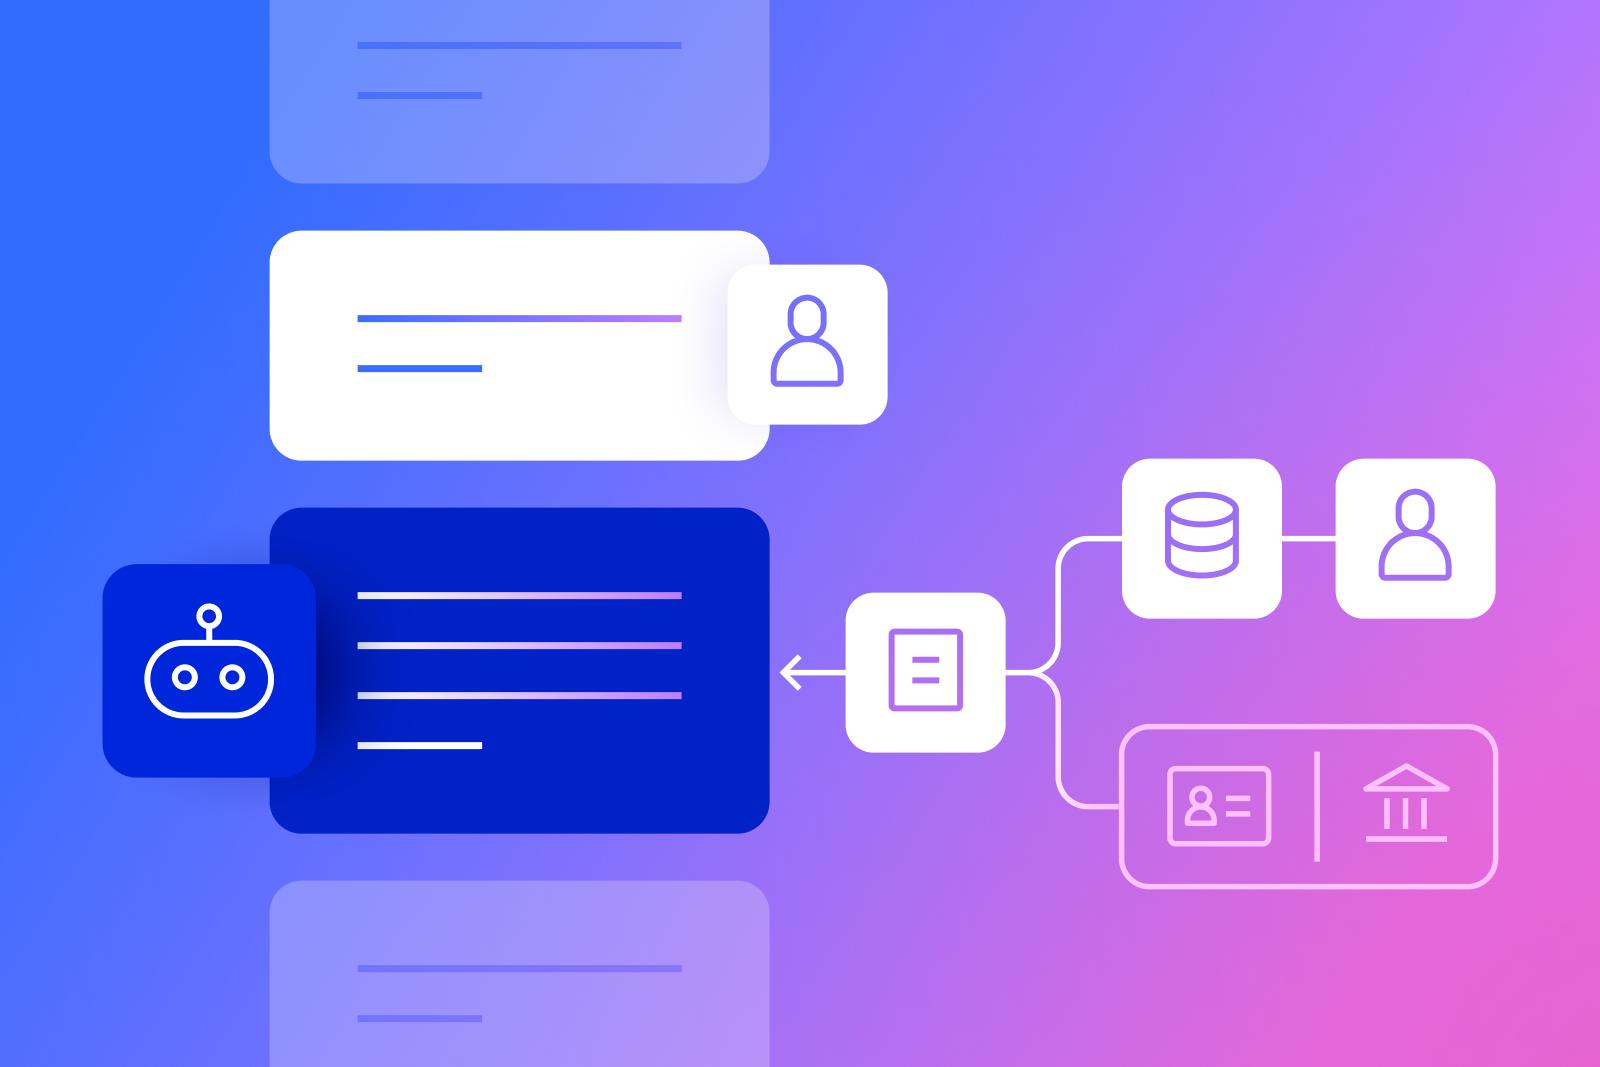

GenAI security refers to the safeguards, controls, and governance practices that protect enterprise data, identities, and workflows when employees use generative AI tools such as ChatGPT, Microsoft Copilot, and Google Gemini. Unlike traditional, model-centric AI security, which is focused on training data, model weights, or adversarial ML, GenAI security concentrates on end-user interaction risks, such as:
Because generative AI is now often integrated with SaaS platforms, productivity suites, and enterprise search, the risk surface expands beyond simple chat interfaces. Employees create custom GPTs, Copilot Studio agents, and Gemini Gems that can access APIs, file repositories, and proprietary datasets.
These autonomous or semi-autonomous components often operate outside central IT’s visibility, introducing shadow AI risks, ungoverned permissions, and the possibility of high-impact data exposure.
Additionally, some GenAI models support web search or web-browsing capabilities. When enabled, portions of a prompt may be incorporated into external search queries processed by third-party services. While not publicly published, this can still lead to unintended data egress and logging outside the enterprise environment.
GenAI security ensures that as organizations scale AI-driven workflows, they preserve confidentiality, maintain compliance, and prevent automated oversharing across distributed teams and systems. To understand why these risks differ from earlier AI paradigms, it’s helpful to contrast GenAI security with traditional, model-centric AI security approaches.
| Dimension | GenAI Security (End-User + Workflow Focus) | Traditional AI Security (Model-Centric) |
|---|---|---|
| Primary Risk Surface | User prompts, AI plugins, custom GPTs/agents, SaaS-AI integrations, identity & permissions | Model architecture, training data pipelines, adversarial ML attacks |
| Core Security Concerns | Data oversharing, unmonitored workflows, shadow AI, prompt-based leakage, unsafe agent actions, web-search data egress | Model poisoning, data integrity, model inversion, secure training environments |
| Control Mechanisms | Identity controls, permission governance, prompt monitoring, DLP, audit logging, workflow oversight | Secure training, dataset validation, adversarial testing, model sandboxing |
| Operational Visibility Needs | Prompt-level insight, agent behavior monitoring, SaaS–LLM data flow mapping, integration tracking | Model behavior explainability, performance monitoring, drift detection |
GenAI environments introduce a blend of familiar security risks and entirely new ones created by end-user prompting, autonomous agent behavior, and deep integrations across SaaS platforms.
Building on the interaction-level concerns outlined earlier, the threats below represent the most common and operationally impactful risks enterprises encounter when GenAI adoption scales.
GenAI tools act on behalf of real users with real permissions. As these tools connect to document repositories, APIs, and SaaS platforms, identity becomes the primary control point that determines what GenAI can access, retrieve, and expose. If permissions are overly broad or poorly understood, GenAI systems can unintentionally amplify access risks.
The most impactful GenAI failures often stem from misaligned or inherited permissions rather than model behavior. Common risks include:
Even when identity is configured correctly, oversharing creates the most frequent leakage events. To reduce exposure, organizations should implement:
Understanding how information moves across systems is also critical. Effective mapping includes:
This visibility enables accurate risk scoring, policy enforcement, and detection of abnormal behavior as GenAI adoption grows.
As GenAI becomes embedded across business workflows, organizations must ensure these tools operate within established regulatory and governance requirements. The following areas reflect the core compliance obligations that must be taken into account for secure GenAI adoption.
Widely recognized standards help ensure consistency, accountability, and regulatory alignment in enterprises seeking to formalize GenAI programs. The following frameworks offer practical guidance for governing GenAI risk, protecting data, and operationalizing responsible AI at scale.
NIST’s AI RMF provides a structured approach for identifying, assessing, and mitigating GenAI risks across the lifecycle. It emphasizes governance functions, continuous monitoring, and documentation to support safe, trustworthy AI deployment.
ISO/IEC 42001 outlines requirements for establishing and maintaining an enterprise AI management system. It helps organizations standardize policies, controls, and oversight practices for GenAI systems operating across different business units.
The EU AI Act enforces obligations tailored to system risk levels, requiring transparency, documentation, and post-market monitoring for higher-risk AI workflows. It directly influences how enterprises evaluate and govern GenAI that interacts with sensitive data or critical processes.
As GenAI adoption accelerates, organizations face several operational hurdles that make consistent governance difficult. These challenges typically arise from distributed use practices, uneven oversight, and the unpredictable nature of AI-assisted workflows:
| Challenge | What Makes It Difficult | Why It Matters for GenAI Security |
|---|---|---|
| Rapid Adoption Across Distributed Teams | Distributed users adopt GenAI tools independently, making it difficult for security teams to track usage or govern custom GPTs, agents, and integrations created outside centralized oversight. | Expanding usage increases blind spots, enabling shadow AI and untracked data access pathways. |
| Limited Visibility into AI Behavior | Many AI actions occur inside chat interfaces, plugins, or autonomous agent workflows, where traditional monitoring tools offer limited insight. | Without prompt-level and agent-level visibility, organizations cannot identify oversharing, misuse, or suspicious AI-driven actions. |
| Inconsistent Policy Enforcement | Different teams apply policies inconsistently across SaaS apps, LLM endpoints, and custom AI components. | Fragmented enforcement leads to unpredictable risk exposure, especially when permissions or data-use rules vary across tools. |
| Balancing Control and Productivity | Strict restrictions can hinder adoption, while lenient controls create governance gaps. Finding the right middle ground is operationally complex. | Organizations must support safe innovation without enabling high-risk workflows or unauthorized data movement. |
With GenAI increasingly embedded in everyday workflows, enterprises need practical controls that reduce risk without slowing adoption. The following best practices help organizations create reliable, scalable safeguards for AI-driven environments.
Since GenAI tools operate differently from traditional IT systems, enterprises increasingly rely on specialized security technologies to manage the risks introduced by GenAI adoption. These tools complement existing controls by providing deeper visibility, stronger governance, and more precise detection capabilities tailored to AI-driven environments.
GenAI risk scoring platforms evaluate the sensitivity, exposure, and business impact of data accessed or generated by AI tools. They help organizations prioritize remediation by identifying high-risk interactions, unsafe agent behaviors, or data flows most likely to lead to leakage or compliance violations.
AI-aware DLP solutions extend traditional data loss prevention capabilities to prompts, outputs, and SaaS–LLM workflows. These tools detect sensitive or regulated information before it’s submitted to a GenAI system and help enforce guardrails that prevent accidental oversharing or external data egress.
Identity governance tools ensure that users, service accounts, and autonomous agents only access data appropriate to their roles. By monitoring entitlements, inheritance patterns, and cross-application identity behavior, these solutions help prevent excessive permissions that could expose sensitive information through GenAI workflows.
Behavioral analytics tools establish baselines for normal GenAI usage and detect anomalies such as unusual data retrieval, unexpected agent actions, or patterns that resemble insider threats. These systems provide contextual insights that help security teams investigate and respond to emerging risks quickly.
Opsin provides an enterprise security platform designed specifically for AI-powered work. It gives security teams unified visibility across ChatGPT, Copilot, Gemini, and related AI-driven workflows while detecting misuse, identifying oversharing, and enforcing AI usage policies consistently across the organization.
Generative AI accelerates productivity but also expands the risk surface across identities, data sources, and AI-assisted workflows. Traditional controls are not designed to handle oversharing, autonomous agents, or web-enabled models, making dedicated GenAI security essential as organizations adopt ChatGPT, Copilot, Gemini, and related tools at scale.
By combining strong governance practices with purpose-built GenAI security platforms, enterprises can embrace AI safely and confidently. Opsin provides the unified visibility, oversight, and contextual risk insights needed to detect unsafe behaviors, identify oversharing, and enforce consistent policies, allowing organizations to innovate with GenAI while keeping sensitive data protected.

Most leaks originate from oversharing, employees unintentionally submitting or retrieving sensitive data via prompts.
• Add real-time prompt scanning for regulated or confidential content.
• Auto-label documents in M365 or Google Workspace to guide user behavior.
• Restrict high-risk prompt categories (e.g., customer data, contracts, PHI).
Opsin’s guide to oversharing in healthcare illustrates this pattern.
Detection requires behavioral baselining across retrieval systems, embeddings, and agent outputs.
Teams must treat web-enabled lookups as potential egress channels requiring policy and logging controls.
Opsin’s Google Gemini security analysis discusses this risk path.
Opsin automatically discovers custom GPTs, Copilot Studio agents, and similar autonomous components across SaaS ecosystems.
Learn how Opsin detects these components at scale.
Opsin monitors prompts, retrieval events, and AI-generated outputs to prevent sensitive data from crossing inappropriate boundaries.